
Exam Name: CompTIA Advanced Security Practitioner (CASP)
Certification Provider: CompTIA
Corresponding Certification: CASP Recertification

Over 170184+ Satisfied Customers
CompTIA Advanced Security Practitioner (CASP): CAS-003 Exam Premium File as PDF & Test Engine

 1250 Customer Reviews
Last Updated: Sep 12, 2026
No. of Questions: 683 Questions & Answers with Testing Engine
Download Limit: Unlimited
Instant Download: Upon successful payment, Our systems will automatically send the product you have purchased to your mailbox by email. (If not received within 12 hours, please contact us. Note: don't forget to check your spam.)
100% Money Back Guarantee
Fast2test has an unprecedented 99.6% first time pass rate among our customers.  We're so confident of our products that we provide no hassle product exchange.
- Best CAS-003 exam practice materials
- Three formats are optional
- 10 years of excellence
- 365 Days Free Updates
- Learn anywhere, anytime
- 100% Safe shopping experience

- Printable CAS-003 PDF Format
- Prepared by CompTIA Experts
- Instant Access to Download CAS-003 PDF
- Study Anywhere, Anytime
- 365 Days Free Updates
- Free CAS-003 PDF Demo Available

- Online Tool, Convenient, easy to study.
- Instant Online Access CAS-003 Dumps
- Supports All Web Browsers
- CAS-003 Practice Online Anytime
- Test History and Performance Review
- Supports Windows / Mac / Android / iOS, etc.

- Installable Software Application
- Simulates Real CAS-003 Exam Environment
- Builds CAS-003 Exam Confidence
- Supports MS Operating System
- Two Modes For CAS-003 Practice
- Practice Offline Anytime
Why wait to start studying? The moment your order is complete, your CAS-003 practice questions land in your inbox within one minute. That is 683 CompTIA Advanced Security Practitioner (CASP) questions, ready when you are.
CompTIA CAS-003 Exam Overview:
| Certification Vendor: | CompTIA |
|---|---|
| Exam Name: | CompTIA Advanced Security Practitioner (CASP+) |
| Exam Number: | CAS-003 |
| Certificate Validity Period: | 3 years |
| Exam Price: | USD ~466–494 (approximate official exam fee) |
| Exam Duration: | 165 minutes |
| Related Certifications: | CompTIA Network+ CompTIA Security+ CompTIA CySA+ |
| Exam Format: | Performance-based, Multiple-choice |
| Passing Score: | Pass/Fail (no scaled score) |
| Real Exam Qty: | Maximum of 90 |
| Available Languages: | Japanese, English |
| Sample Questions: | CompTIA CAS-003 Sample Questions |
| Exam Way: | Onsite at Pearson VUE or Online proctored (Pearson VUE OnVUE). |
| Pre Condition: | Recommended: 10 years of IT administration experience with at least 5 years of hands-on security experience; recommended but not mandatory to hold Security+, Network+, or CySA+ (experience based). |
| Official Syllabus URL: | https://www.comptia.org/en-us/certifications/casp |
CompTIA CAS-003 Exam Syllabus Topics:
| Section | Weight | Objectives |
|---|---|---|
| Topic 1: Enterprise Security Architecture | 25% | - Network & security components integration - Host device security controls - Mobile & small device security controls - Application security & vulnerabilities |
| Topic 2: Research, Development and Collaboration | 13% | - Security activities across technology lifecycle - Interdisciplinary collaboration for security goals - Research industry trends & impact |
| Topic 3: Risk Management | 19% | - Risk mitigation strategies & controls - Risk metric analysis - Security, privacy policies & procedures - Business and industry influences & security risks |
| Topic 4: Enterprise Security Operations | 20% | - Incident response & recovery procedures - Security tools selection - Security assessment methods |
| Topic 5: Technical Integration of Enterprise Security | 23% | - Advanced authentication & authorization - Cloud & virtualization security - Host, storage, network, application integration - Cryptographic techniques implementation |
Your CompTIA Advanced Security Practitioner (CASP) Questions, Answered
The CAS-003 exam, officially titled CompTIA Advanced Security Practitioner (CASP), is the qualifying test for the CASP Recertification certification from CompTIA, a credential at the Advanced / Expert level. Passing it proves you have the skills employers look for in certified professionals, and it can also support progress toward related credentials such as CompTIA Security+, CompTIA Network+, CompTIA CySA+.
The CompTIA Advanced Security Practitioner (CASP) exam gives you 165 minutes to work through Maximum of 90 questions. That is a steady pace with little room for second-guessing, so train yourself to read each question once, flag the difficult ones, and keep moving. Before exam day, sit at least two full timed sessions in the Fast2test test engine — when the clock feels familiar, it stops being a threat.
You need Pass/Fail (no scaled score) to pass, and the official registration fee is USD ~466–494 (approximate official exam fee). Fall short and you pay that fee in full again for every retake, which makes solid preparation the cheaper option by far. Work through the Fast2test practice questions until you score comfortably above the passing mark, then book your seat.
Recommended: 10 years of IT administration experience with at least 5 years of hands-on security experience; recommended but not mandatory to hold Security+, Network+, or CySA+ (experience based). Eligibility rules can change over time, so before you register, confirm the latest requirements on the official exam page: CompTIA CAS-003 exam overview.
Yes. Fast2test offers a free PDF demo for the CompTIA Advanced Security Practitioner (CASP) exam so you can judge the quality of our questions and answers before paying anything. Every purchase also comes with 365 days of free updates, and once that period expires you can extend your update service at a 50% discount.
Your purchase is protected by a 100% money-back guarantee. If you sit the corresponding CAS-003 exam within 60 days of buying and do not pass, send us a scan of your exam enrollment slip together with your official Score Report (PDF) within 2 days of the exam date — the candidate name must match the payer's name — and we will process your full refund within 7 days. Please note that exams taken within 3 days of purchase, materials downloaded without ever sitting the exam, free products, and expired orders are not covered. If you would rather not have a refund, you can exchange your order for two exam products of equal value, free of charge, and keep the update service on your original purchase.
Delivery is instant: your files are emailed to you within one minute of payment and can also be downloaded directly, with no limit on the number of computers you install them on. If nothing has arrived within 2 hours, contact our customer service team and we will sort it out.
The CompTIA Advanced Security Practitioner (CASP) syllabus is organized into 5 domains. The main areas include Risk Management (19%), Enterprise Security Operations (20%), and Technical Integration of Enterprise Security (23%). Scroll up to the Exam Topics section above for the complete, current outline before you plan your study schedule.
CompTIA Advanced Security Practitioner (CASP) Sample Questions:
A security administrator is updating a company's SCADA authentication system with a new application. To ensure interoperability between the legacy system and the new application, which of the following stakeholders should be involved in the configuration process before deployment? (Choose two.)
- A. Service desk personnel
- B. Compliance manager
- C. Human resources administrator
- D. Network engineer
- E. Facilities manager
- F. Incident response coordinator
Correct Answer: B,F 🗳️
The Chief Information Security Officer (CISO) has asked the security team to determine whether the organization is susceptible to a zero-day exploit utilized in the banking industry and whether attribution is possible. The CISO has asked what process would be utilized to gather the information, and then wants to apply signatureless controls to stop these kinds of attacks in the future. Which of the following are the MOST appropriate ordered steps to take to meet the CISO's request?
- A. 1. Obtain the latest IOCs from the open source repositories2. Perform a sweep across the network to identify positive matches3. Sandbox any suspicious files4. Notify the CERT team to apply a future proof threat model
- B. 1. Analyze the current threat intelligence2. Utilize information sharing to obtain the latest industry IOCs3. Perform a sweep across the network to identify positive matches4. Apply machine learning algorithms
- C. 1. Perform the ongoing research of the best practices2. Determine current vulnerabilities and threats3. Apply Big Data techniques4. Use antivirus control
- D. 1. Apply artificial intelligence algorithms for detection2. Inform the CERT team3. Research threat intelligence and potential adversaries4. Utilize threat intelligence to apply Big Data techniques
Correct Answer: A 🗳️
A video-game developer has received reports of players who are cheating. All game players each have five capabilities that are ranked on a scale of 1 to 10 points, with 10 total points available for balance. Players can move these points between capabilities at any time The programming logic is as follows:
* A player asks to move points from one capability to another
* The source capability must have enough points to allow the move
* The destination capability must not exceed 10 after the move
* The move from source capability to destination capability is then completed The time stamps of the game logs show each step of the transfer process takes about 900ms However, the time stamps of the cheating players show capability transfers at the exact same time. The cheating players have 10 points in multiple capabilities. Which of the following is MOST likely being exploited to allow these capability transfers?
- A. CSRF
- B. Integer overflow
- C. TOC/TOU
- D. XSS
- E. Memory leak
- F. SQL injection
Correct Answer: B 🗳️
A security engineer is assessing the controls that are in place to secure the corporate-Internet-facing DNS server. The engineer notices that security ACLs exist but are not being used properly. The DNS server should respond to any source but only provide information about domains it has authority over. Additionally, the DNS administrator have identified some problematic IP addresses that should not be able to make DNS requests. Given the ACLs below: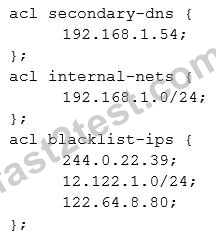
Which of the following should the security administrator configure to meet the DNS security needs?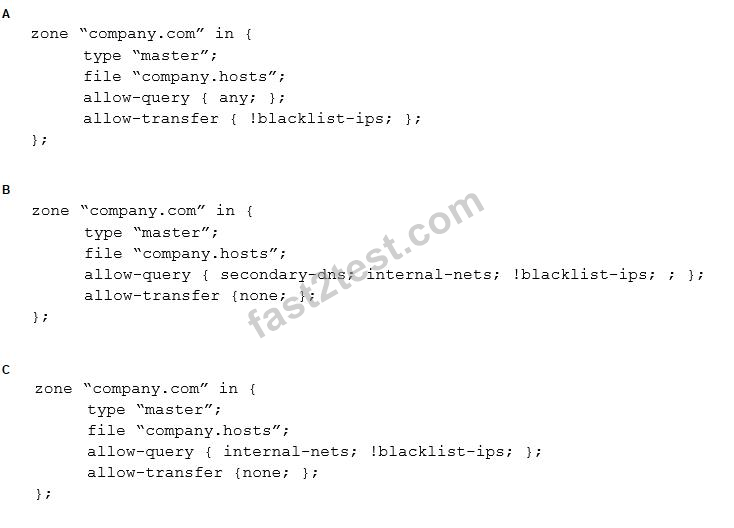
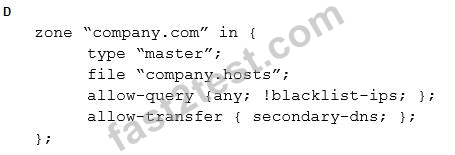
- A. Option B
- B. Option A
- C. Option D
- D. Option C
Correct Answer: C 🗳️
At a meeting, the systems administrator states the security controls a company wishes to implement seem excessive, since all of the information on the company's web servers can be obtained publicly and is not proprietary in any way. The next day the company's website is defaced as part of an SQL injection attack, and the company receives press inquiries about the message the attackers displayed on the website.
Which of the following is the FIRST action the company should take?
- A. Establish chain of custody for all systems to which the systems administrator has access.
- B. Conduct a detailed forensic analysis of the compromised system.
- C. Refer to and follow procedures from the company's incident response plan.
- D. Call a press conference to explain that the company has been hacked.
- E. Inform the communications and marketing department of the attack details.
Correct Answer: C 🗳️
1250 Customer ReviewsCustomers Feedback (* Some similar or old comments have been hidden.)
Fast2test is the only credible source for passing Exam CAS-003!
Chad

I just come to inform you that i have passed CAS-003 exam yesterday!I feel so wonderful and it is all your efforts that helped me. Thank you, my friends!
Matt
Passed my CAS-003 exam 3 days ago with a high score. Highly recomend. Big thanks!
Poppy

Awesome pdf files and exam practise software by Fast2test. I scored a 93% marks in the CAS-003 certification exam. Highly suggested to all.
Shirley
With this valid CAS-003 learning questions, i can put the efforts to the positive result and be ready for the exam. I have achieved the certification. Thanks!
Heloise
Passed CAS-003 exams today with a joyful score. Your CAS-003 study materials are very good for the people who do not have much time for their exam preparation. Thanks for your help.
Grover
Thanks a lot! The CAS-003 practice test has helped me a lot in learning CAS-003 course and also in passing the test.
Andy
Practice more and more with PDF, APP, SOFT, i can clear my CAS-003 exam easily
Lindsay
Thanks for updated dump. Yesterday i have completed my certification. 100% recommended for CAS-003 exam
Theobald
I received the downloading link and password about ten minutes after paying for CAS-003 test materials, and I had a practice in the day I received CAS-003 practicing materials.
Ingemar
All credit of my success in exam CAS-003 goes to Fast2test study guide. This amazing guide is full of information and the content is simplified to the level of average candidatte dumps Always Incredible!
Abraham
The updated CompTIA Advanced Security Practitioner answers are correct this time.
Rachel
I passed the CAS-003 exam though i still didn't understand some of them, anyway it is valid to pass with this CAS-003 practice questions.
Maud
Thank you for your help! Your CAS-003 exam dumps are easy-understanding. I just used your study guide for my CAS-003 examination and passed exam.
Norton
It is on the top and it caters all the requirements and helps students in memorizing the important topics for taking CAS-003 exam.
Gabriel
During my net surfing, I stumbled on Fast2test Study Guide free demo. It impressed me so much that I decided to make Fast2test guide my source of exam preparation. Very helpful!!!
Blithe
I found the CAS-003 study material to be a good value. I passed the CAS-003 with it. Fast2test exam material is the most important material which you need to have prepared for your CAS-003 exam. Recommend!
Nathan
Just study CAS-003 questions three days, this is all my need to make it pass CAS-003 exam. Now going for other exam in next 9 days, I will choose Fast2test too. Good webaite!
Amanda
I passed my CAS-003 exam with preparing for it for about a week, carefully studied the CAS-003 exam dumps and the questions are almost all from the CAS-003 exam dumps. Very helpful!
Linda
Instant Download CAS-003
After Payment, our system will send you the products you purchase in mailbox in a minute after payment. If not received within 2 hours, please contact us.
365 Days Free Updates
Free update is available within 365 days after your purchase. After 365 days, you will get 50% discounts for updating.

Money Back Guarantee
Full refund if you fail the corresponding exam in 60 days after purchasing. And Free get any another product.
Security & Privacy
We respect customer privacy. We use McAfee's security service to provide you with utmost security for your personal information & peace of mind.
Related Exams
Related Posts
Contact Us
If you have any question please leave me your email address, we will reply and send email to you in 12 hours.
Our Working Time: ( GMT 0:00-15:00 ) From Monday to Saturday
Support: Contact now