
Exam Name: Certified Kubernetes Security Specialist (CKS)
Certification Provider: Linux Foundation
Corresponding Certification: Kubernetes Security Specialist

Over 171466+ Satisfied Customers
Certified Kubernetes Security Specialist (CKS): CKS Exam Premium File as PDF & Test Engine

 999 Customer Reviews
Last Updated: Nov 07, 2026
No. of Questions: 66 Questions & Answers with Testing Engine
Download Limit: Unlimited
Instant Download: Upon successful payment, Our systems will automatically send the product you have purchased to your mailbox by email. (If not received within 12 hours, please contact us. Note: don't forget to check your spam.)
100% Money Back Guarantee
Fast2test has an unprecedented 99.6% first time pass rate among our customers.  We're so confident of our products that we provide no hassle product exchange.
- Best CKS exam practice materials
- Three formats are optional
- 10 years of excellence
- 365 Days Free Updates
- Learn anywhere, anytime
- 100% Safe shopping experience

- Printable CKS PDF Format
- Prepared by Linux Foundation Experts
- Instant Access to Download CKS PDF
- Study Anywhere, Anytime
- 365 Days Free Updates
- Free CKS PDF Demo Available

- Online Tool, Convenient, easy to study.
- Instant Online Access CKS Dumps
- Supports All Web Browsers
- CKS Practice Online Anytime
- Test History and Performance Review
- Supports Windows / Mac / Android / iOS, etc.

- Installable Software Application
- Simulates Real CKS Exam Environment
- Builds CKS Exam Confidence
- Supports MS Operating System
- Two Modes For CKS Practice
- Practice Offline Anytime
Why Choose Linux Foundation CKS Exam on Fast2test
Fast2test is suitable for busy professional, who can know prepare for Certification exam in a week. Our CKS practice materials has been prepared by the team of Linux Foundation experts after an in-depth analysis of vendor recommended syllabus. Now you can pass Linux Foundation certification exam with our CKS study material on the first attempt.
CKS exam is an important Linux Foundation Certification which can test your professional skills. Candidates want to pass the exam successfully to prove their competence. Fast2test Linux Foundation technical experts have collected and certified 66 questions and answers of Kubernetes Security Specialist - Certified Kubernetes Security Specialist (CKS) which are designed to cover the knowledge points of the Planning and Designing Linux Foundation Superdome Server Solutions and enhance candidates' abilities. With Fast2test CKS preparation tests you can pass the Kubernetes Security Specialist - Certified Kubernetes Security Specialist (CKS) easily, get the Linux Foundation certification and go further on Linux Foundation career path.
Prompt Updates on CKS
Once there is some changes on CKS exam, we will update the study materials timely to make them be consistent with the current exam. We devote to giving our customers the best and latest Linux Foundation CKS dumps. Besides, the product you buy will be updated in time within 365 Days for free.
100% Guarantee to Pass Your CKS Exam
If you do not pass the Linux Foundation Kubernetes Security Specialist CKS exam (Certified Kubernetes Security Specialist (CKS)) on your first attempt using our Fast2test testing engine, we will give you a FULL REFUND of your purchasing fee.
Linux Foundation CKS Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
| Topic 5 |
|
Reference: https://training.linuxfoundation.org/certification/certified-kubernetes-security-specialist/#exams
Downloadable, Interactive CKS Testing engines
Our Certified Kubernetes Security Specialist (CKS) Preparation Material provides you everything you will need to take a Linux Foundation Kubernetes Security Specialist CKS examination. Details are researched and produced by Linux Foundation Certification Experts who are constantly using industry experience to produce precise, and logical.
Quality and Value for the CKS Exam
Fast2test Practice Exams for Linux Foundation Kubernetes Security Specialist CKS are written to the highest standards of technical accuracy, using only certified subject matter experts and published authors for development.
Linux Foundation Certified Kubernetes Security Specialist (CKS) Sample Questions:
SIMULATION
Cluster: qa-cluster
Master node: master Worker node: worker1
You can switch the cluster/configuration context using the following command:
[desk@cli] $ kubectl config use-context qa-cluster
Task:
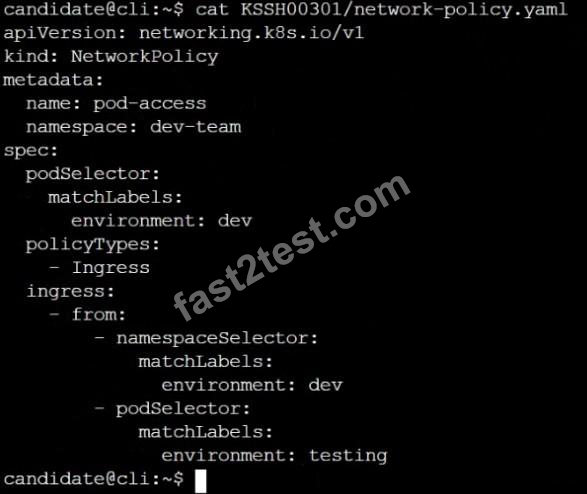
Create a NetworkPolicy named restricted-policy to restrict access to Pod product running in namespace dev.
Only allow the following Pods to connect to Pod products-service:
1. Pods in the namespace qa
2. Pods with label environment: stage, in any namespace
Correct Answer:
See the Explanation belowExplanation:


SIMULATION
Context
Your organization's security policy includes:
ServiceAccounts must not automount API credentials
ServiceAccount names must end in "-sa"
The Pod specified in the manifest file /home/candidate/KSCH00301 /pod-m nifest.yaml fails to schedule because of an incorrectly specified ServiceAccount.
Complete the following tasks:
Task
1. Create a new ServiceAccount named frontend-sa in the existing namespace qa. Ensure the ServiceAccount does not automount API credentials.
2. Using the manifest file at /home/candidate/KSCH00301 /pod-manifest.yaml, create the Pod.
3. Finally, clean up any unused ServiceAccounts in namespace qa.
Correct Answer:
See the Explanation below
Explanation:


SIMULATION
You must complete this task on the following cluster/nodes:
Cluster: trace
Master node: master
Worker node: worker1
You can switch the cluster/configuration context using the following command:
[desk@cli] $ kubectl config use-context trace
Given: You may use Sysdig or Falco documentation.
Task:
Use detection tools to detect anomalies like processes spawning and executing something weird frequently in the single container belonging to Pod tomcat.
Two tools are available to use:
1. falco
2. sysdig
Tools are pre-installed on the worker1 node only.
Analyse the container's behaviour for at least 40 seconds, using filters that detect newly spawning and executing processes.
Store an incident file at /home/cert_masters/report, in the following format:
[timestamp],[uid],[processName]
Note: Make sure to store incident file on the cluster's worker node, don't move it to master node.
Correct Answer:
See the Explanation below
Explanation:
$vim /etc/falco/falco_rules.local.yaml
- rule: Container Drift Detected (open+create)
desc: New executable created in a container due to open+create
condition: >
evt.type in (open,openat,creat) and
evt.is_open_exec=true and
container and
not runc_writing_exec_fifo and
not runc_writing_var_lib_docker and
not user_known_container_drift_activities and
evt.rawres>=0
output: >
%evt.time,%user.uid,%proc.name # Add this/Refer falco documentation
priority: ERROR
$kill -1 <PID of falco>
Explanation:
[desk@cli] $ ssh node01
[node01@cli] $ vim /etc/falco/falco_rules.yaml
search for Container Drift Detected & paste in falco_rules.local.yaml
[node01@cli] $ vim /etc/falco/falco_rules.local.yaml
- rule: Container Drift Detected (open+create)
desc: New executable created in a container due to open+create
condition: >
evt.type in (open,openat,creat) and
evt.is_open_exec=true and
container and
not runc_writing_exec_fifo and
not runc_writing_var_lib_docker and
not user_known_container_drift_activities and
evt.rawres>=0
output: >
%evt.time,%user.uid,%proc.name # Add this/Refer falco documentation
priority: ERROR
[node01@cli] $ vim /etc/falco/falco.yaml
SIMULATION
Documentation Deployments, Pods, bom Command Help bom-help
You must connect to the correct host. Failure to do so may result in a zero score.
[candidate@base] $ ssh cks000035
Task
The alpine Deployment in the alpine namespace has three containers that run different versions of the alpine image.
First, find out which version of the alpine image contains the libcrypto3 package at version 3.1.4-r5.
Next, use the pre-installed bom tool to create an SPDX document for the identified image version at /home/candidate/alpine.spdx.
You can find the bom tool documentation at bom.
Finally, update the alpine Deployment and remove the container that uses the idenfied image version.
The Deployment's manifest file can be found at /home/candidate/alpine-deployment.yaml.
Do not modify any other containers of the Deployment.
Correct Answer:
See the Explanation below for complete solution
Explanation:
1) Connect to the correct host
ssh cks000035
sudo -i
export KUBECONFIG=/etc/kubernetes/admin.conf
2) List the 3 container names + images in the Deployment
kubectl -n alpine get deploy alpine -o jsonpath='{range .spec.template.spec.containers[*]}{.name}{"\t"}{.image}{"\n"}{end}' You'll get 3 lines like:
c1 alpine:3.xx
c2 alpine:3.yy
c3 alpine:3.zz
3) Identify which alpine image has libcrypto3 at 3.1.4-r5
Fastest reliable method (since it's Alpine, just query apk inside each image):
Run these one-by-one for each image you saw in step 2:
docker run --rm <ALPINE_IMAGE_1> sh -c 'apk info -v libcrypto3 2>/dev/null | head -n1' docker run --rm <ALPINE_IMAGE_2> sh -c 'apk info -v libcrypto3 2>/dev/null | head -n1' docker run --rm <ALPINE_IMAGE_3> sh -c 'apk info -v libcrypto3 2>/dev/null | head -n1'
✅ The correct image is the one that prints exactly:
libcrypto3-3.1.4-r5
Note that full image tag, e.g.:
IMG=alpine:3.xx
4) Create SPDX document with bom for that identified image
(Use the identified image from step 3.)
bom generate --image $IMG --format spdx --output /home/candidate/alpine.spdx Verify file exists:
ls -l /home/candidate/alpine.spdx
5) Remove ONLY the container that uses that image version
The manifest to edit is:
vi /home/candidate/alpine-deployment.yaml
In the spec.template.spec.containers: list, find the container entry whose image: equals the identified $IMG, and delete that one container block only (name/image/ports/etc for that container).
Save:
:wq
6) Apply the updated Deployment (do not change other containers)
kubectl apply -f /home/candidate/alpine-deployment.yaml
Wait rollout:
kubectl -n alpine rollout status deployment/alpine
7) Verify only 2 containers remain
kubectl -n alpine get deploy alpine -o jsonpath='{range .spec.template.spec.containers[*]}{.name}{"\t"}{.image}{"\n"}{end}' You should now see 2 lines, and the $IMG line should be gone.
If bom generate ... errors (quick fix)
Check exact syntax on that system:
bom --help
bom generate --help
Then rerun with the flags it expects, keeping:
image = $IMG
output = /home/candidate/alpine.spdx
format = spdx
SIMULATION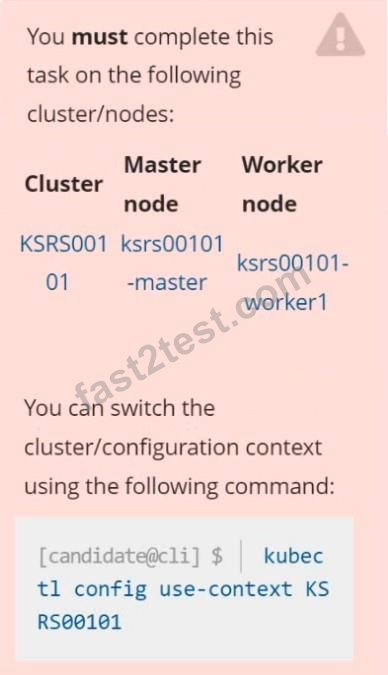

Two tools are pre-installed on the cluster's worker node:
Using the tool of your choice (including any non pre-installed tool), analyze the container's behavior for at least 30 seconds, using filters that detect newly spawning and executing processes.
Store an incident file at /opt/KSRS00101/alerts/details, containing the detected incidents, one per line, in the following format:
The following example shows a properly formatted incident file: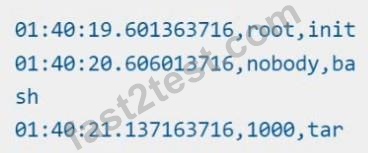


Correct Answer:
See explanation below
Explanation:


Viewing page 1 out of 14 pages.
Viewing questions 1-5 out of 66 questions.
999 Customer ReviewsCustomers Feedback (* Some similar or old comments have been hidden.)
Just passed. 98 % score. Thanks to Fast2test. This Linux Foundation CKS dumps is valid but not complete. Exam guide is 100% valid.
Chester
The CKS material was the essential component in me passing the CKS exam. I purchased it and then passed the exam with a good score. Thanks.
Len
If I call CKS study materials immensely useful, I’m not wrong! I have passed my exam with CKS dump's help.
Bing

The CKS training dump which is the latest also is the most valid and useful. I passed the exam with a high score. Never doubt about it! Just buy it!
Buck

CKS is my next exam.
Albert
I passed my certified CKS exam with 95% marks. I used the material by Fast2test and it was so easy to learn from it. Great work team Fast2test. Highly suggested to all.
Quentin
Fast2test exam dumps for the CKS certification exam are the latest. Highly recommended to all taking this exam. I scored 94% marks in the exam. Thank you Fast2test.
Alberta
Your guys did a good job. Love to use Fast2test study materials, I passed the exam easily. Thank you.
Sabrina
CKS study dumps were so comprehensive and easy to understand that I passed the CKSexam with flying colors on my first attempt.
Broderick
I am going to take this CKS exam , could you pls send me some sample questions to test?
Adrian
Highly recommend Fast2test pdf exam guide to all those taking the CKS exam. I had less time to prepare for the exam but Fast2test made me learn very quickly.
Robin
I have passed CKS exam with their CKS exam dumps. Thanks a million! Today i passed the CKS exam highly with 96% marks!
Yvette
After purchase for the CKS study guide,I recived it , studied then I took the CKS exam and passed. It is really helpful! Don't try to doubt about it! Just believe it and you will pass!
Maxine
I have no classes on CKS exam, but I want to pass it so that I will be more competitive when I have to find a job after gratuation. With your CKS learning guide, I have got my certification now. Wise choice!
Arno
The demo of the CKS exam guide is the real questions and answers of the the whole materials. From it, i know it is the right thing i need. Passed the exam yesterday!
Agatha
Instant Download CKS
After Payment, our system will send you the products you purchase in mailbox in a minute after payment. If not received within 2 hours, please contact us.
365 Days Free Updates
Free update is available within 365 days after your purchase. After 365 days, you will get 50% discounts for updating.

Money Back Guarantee
Full refund if you fail the corresponding exam in 60 days after purchasing. And Free get any another product.
Security & Privacy
We respect customer privacy. We use McAfee's security service to provide you with utmost security for your personal information & peace of mind.
Related Exams
Related Posts
Contact Us
If you have any question please leave me your email address, we will reply and send email to you in 12 hours.
Our Working Time: ( GMT 0:00-15:00 ) From Monday to Saturday
Support: Contact now