

[2021] Pass Microsoft MS-101 Test Practice Test Questions Exam Dumps
Verified MS-101 dumps Q&As - MS-101 dumps with Correct Answers
Other MS-101 Exam Details and Training Options to Use
Now when you know the skills you must develop, you should know the exam details as well. Thus, you’ll need to complete 40-60 questions within 180 minutes. For that, prep process is vital and it is the time to know more about the testing process itself and study materials you can utilize to succeed. First of all, remember to register for your exam saving several weeks for revision and pay an enrollment fee of $165. Then, follow the official training course offered by Microsoft to learn the basics and refer to various books and videos. Also, make use of practice tests to monitor your progress and check whether you still have any knowledge gaps to be filled. If the results of your trial attempts with mocks are good, then you can be sure you are ready to face your MS-101!
NEW QUESTION 95
From the Security & Compliance admin center, you create a retention policy named Policy1.
You need to prevent all users from disabling the policy or reducing the retention period.
Which command should you run? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation: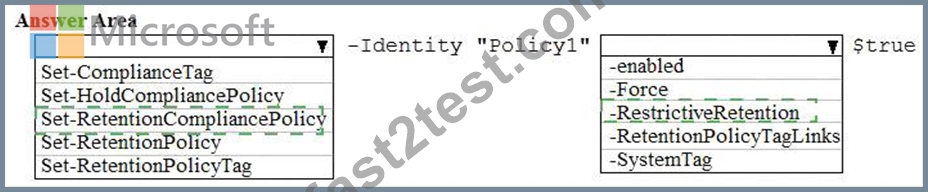
Explanation
References:
https://docs.microsoft.com/en-us/powershell/module/exchange/policy-and-compliance-retention/set-retentioncom
NEW QUESTION 96
HOTSPOT
You have a Microsoft 365 subscription that contains the users shown in the following table.
You run the following cmdlet.
Set-MailboxAuditBypassAssociation -Identity User2
-AuditByPassEnabled $true
The users perform the following actions:
* User1 accesses an item in the mailbox of User2.
* User2 modifies a mailbox item in the mailbox of User3.
* User3 signs in to her mailbox.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Hot Area:
Answer:
Explanation: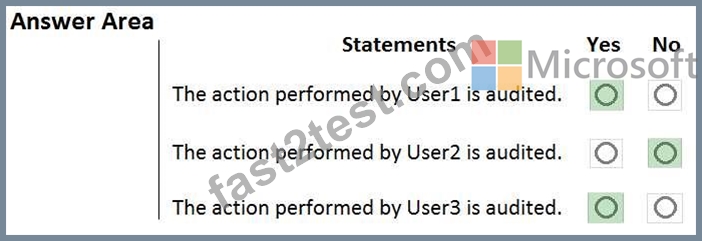
Section: [none]
Explanation/Reference:
https://docs.microsoft.com/en-us/powershell/module/exchange/set-mailboxauditbypassassociation?
view=exchange-ps
NEW QUESTION 97
You have a Microsoft 365 subscription that contains the alerts shown in the following table.
Which properties of the alerts can you modify?
- A. Status and Comment only
- B. Status, Severity, Comment and Category
- C. Status, Severity, and Comment only
- D. Status only
- E. Status and Severity only
Answer: A
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/security/defender-endpoint/update-alert?view=o365-worldwide#
NEW QUESTION 98
You use Windows Defender Advanced Threat Protection (Windows Defender ATP).
You have the Windows Defender ATP machine groups shown in the following table.
You plan to onboard computers to Windows Defender ATP as shown in the following table.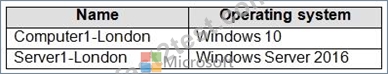
To which machine group will each computer be added? To answer, select the appropriate options in the answer are.
NOTE: Each correct selection is worth one point.
Answer:
Explanation: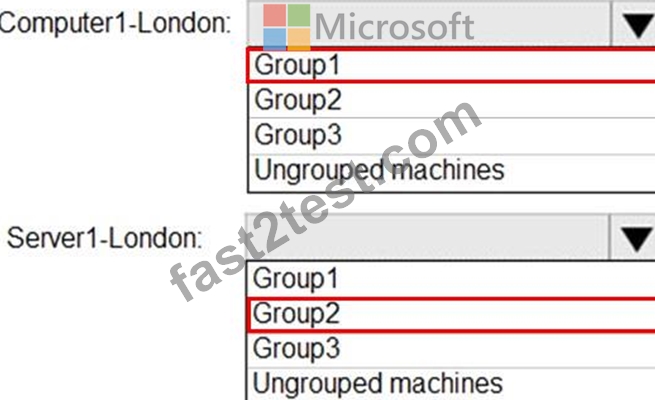
NEW QUESTION 99
You implement Microsoft Azure Advanced Threat Protection (Azure ATP).
You have an Azure ATP sensor configured as shown m the following exhibit.
How long after the Azure ATP cloud service is updated will the sensor update?
- A. 1 hour
- B. 4 hours
- C. 7days
- D. 48 hours
- E. 12 hours
Answer: A
NEW QUESTION 100 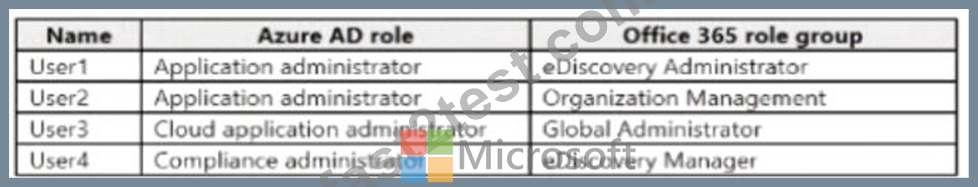
You have an eDiscovery case shown in the follow table.
For each of the following statements select yes of the statements is true. Otherwise, select NO.
NOTE: each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION 101
You have a Microsoft 365 subscription that contains a Microsoft SharePoint Online site named Site1. Site1 has he files in the following table.
The Site1 users are assigned the roles shown in the following table.
You create a data less prevention (DLP) policy names Policy1 as shown in the following exhibit.
How many files will be visible to user1 and User2 after Policy' is applied to answer, selected select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
NEW QUESTION 102
You have a Microsoft 365 subscription.
All users have their email stored in Microsoft Exchange Online.
In the mailbox of a user named User1, you need to preserve a copy of all the email messages that contain the word Project X.
What should you do first?
- A. From the Security & Compliance admin center, create a label and label policy.
- B. From the Exchange admin center, start a mail flow message trace
- C. From the Security & Compliance admin center, create, create a label and a label policy.
- D. From the Security & Compliance admin center, start a message trace.
- E. From the Security & Compliance admin center, create a data loss prevention (DLP) policy.
Answer: E
Explanation:
Explanation
A DLP policy contains a few basic things:
Where to protect the content: locations such as Exchange Online, SharePoint Online, and OneDrive for Business sites, as well as Microsoft Teams chat and channel messages.
When and how to protect the content by enforcing rules comprised of:
Conditions the content must match before the rule is enforced. For example, a rule might be configured to look only for content containing Social Security numbers that's been shared with people outside your organization.
Actions that you want the rule to take automatically when content matching the conditions is found. For example, a rule might be configured to block access to a document and send both the user and compliance officer an email notification.
References:
https://docs.microsoft.com/en-us/microsoft-365/compliance/data-loss-prevention-policies
NEW QUESTION 103
You have a Microsoft Azure Active Directory (Azure AD) tenant named contoso.onmicrosoft.com.
You have a Microsoft 365 subscription.
You need to ensure that users can manage the configuration settings for all the Windows 10 devices in your organization.
What should you configure?
- A. the Exchange on-premises access settings
- B. the Enrollment restrictions
- C. the Windows enrollment settings
- D. the mobile device management (MDM) authority
Answer: D
Explanation:
Explanation/Reference:
References:
https://docs.microsoft.com/en-us/intune/mdm-authority-set
NEW QUESTION 104
You have a Microsoft 365 subscription.
You need to implement Windows Defender Advanced Threat Protection (ATP) for all the supported devices enrolled in mobile device management (MDM).
What should you include in the device configuration profile? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.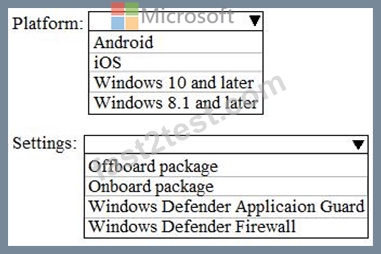
Answer:
Explanation: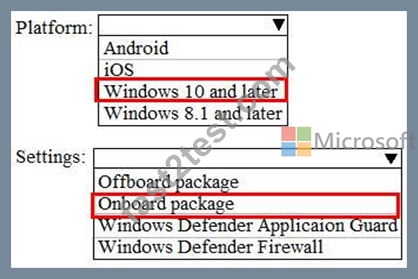
References:
https://docs.microsoft.com/en-us/intune/advanced-threat-protection
NEW QUESTION 105
HOTSPOT
Your company uses Microsoft Defender Advanced Threat Protection (ATP). Microsoft Defender ATP contains the device groups shown in the following table.
You onboard computers to Microsoft Defender ATP as shown in the following table.
Of which groups are Computer1 and Computer2 members? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Hot Area: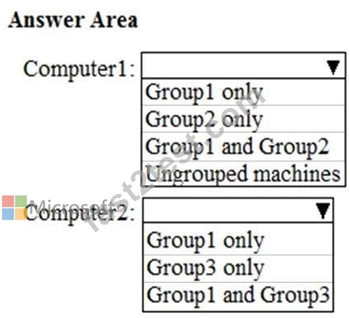
Answer:
Explanation:
Section: [none]
Explanation:
When a device is matched to more than one group, it is added only to the highest ranked group.
Reference:
https://docs.microsoft.com/en-us/microsoft-365/security/defender-endpoint/machine-groups?view=o365- worldwide
NEW QUESTION 106
You have a Microsoft 365 subscription.
You have the devices shown in the following table.
You need to onboard the devices to Windows Defender Advanced Threat Protection (ATP). The solution must avoid installing software on the devices whenever possible.
Which onboarding method should you use for each operating system? To answer, drag the appropriate methods to the correct operating systems. Each method may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.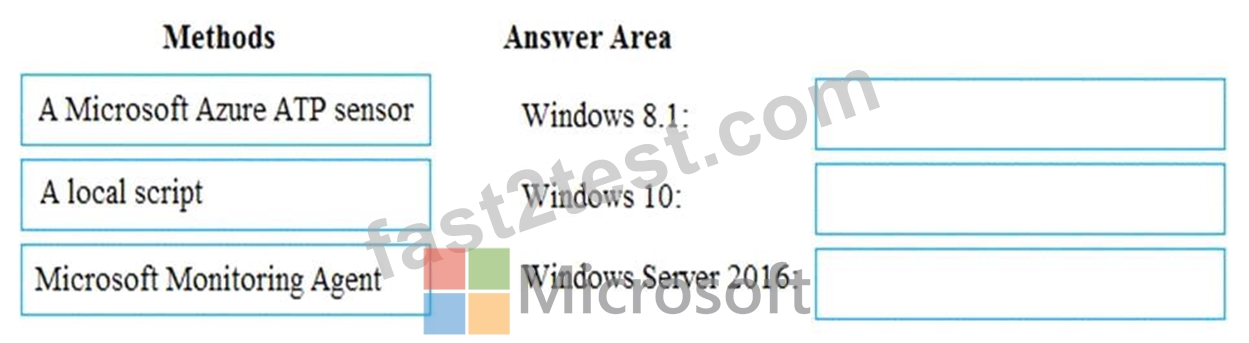
Answer:
Explanation:
Explanation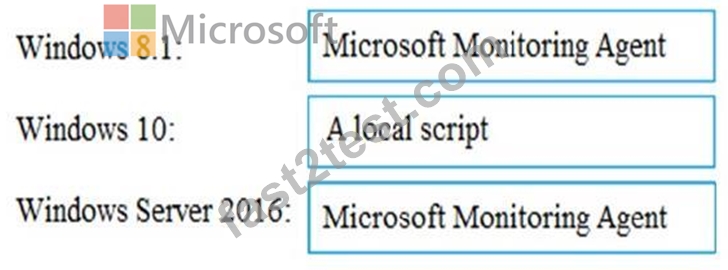
References:
https://docs.microsoft.com/en-us/windows/security/threat-protection/windows-defender-atp/onboard-downlevel-
https://docs.microsoft.com/en-us/windows/security/threat-protection/windows-defender-atp/configure-endpoints-
https://docs.microsoft.com/en-us/windows/security/threat-protection/windows-defender-atp/configure-server-end
NEW QUESTION 107
You have the Microsoft Azure Advanced Threat Protection (ATP) workspace shown in the Workspace exhibit. (Click the Workspace tab.)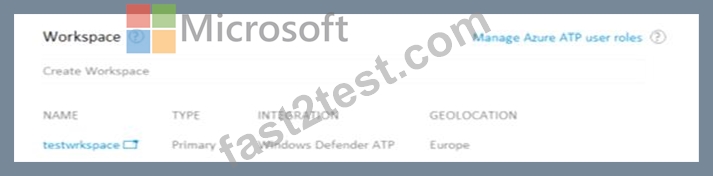
The sensors settings for the workspace are configured as shown in the Sensors exhibit. (Click the Sensors tab.)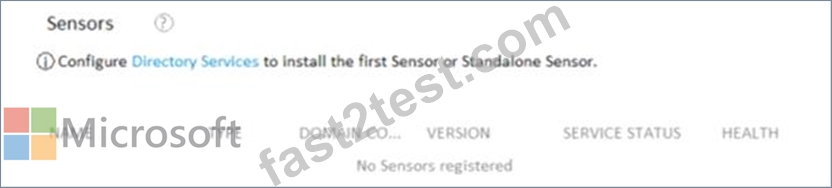
You need to ensure that Azure ATP stores data in Asia.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.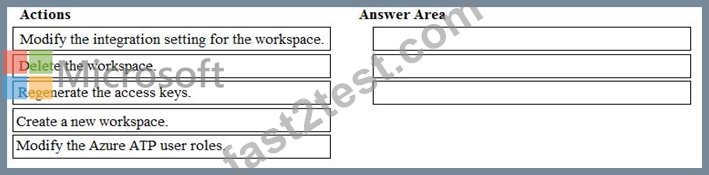
Answer:
Explanation: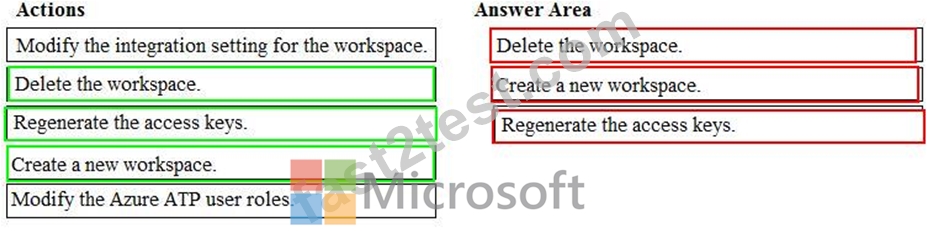
https://docs.microsoft.com/en-us/azure-advanced-threat-protection/install-atp-step1
NEW QUESTION 108
You have a Microsoft 365 subscription.
You plan to connect to Microsoft Exchange Online PowerShell and run the following cmdlets:
* Search-MailboxAuditLog
* Test-ClientAccessRule
* Set-GroupMailbox
* Get-Mailbox
Which cmdlet will generate an entry in the Microsoft Office 365 audit log?
- A. Set-GroupMailbox
- B. Search-MailboxAuditLog
- C. Test-ClientAccessRule
- D. Get-Mailbox
D18912E1457D5D1DDCBD40AB3BF70D5D
Answer: A
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/search-the-audit-log-in-security-and-compliance?vie
NEW QUESTION 109
You have a Microsoft 365 subscription.
You create a Microsoft Cloud App Security policy named Risk1 based on the Logon from a risky IP address template as shown in the following exhibit.
You have two users named User1 and User2. Each user signs in to Microsoft SharePoint Online from a risky IP address 10 times within 24 hours.
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION 110
You implement Microsoft Azure Advanced Threat Protection (Azure ATP).
You have an Azure ATP sensor configured as shown in the following exhibit.
How long after the Azure ATP cloud service is updated will the sensor update?
- A. 20 hours
- B. 48 hours
- C. 7 hours
- D. 12 hours
Answer: D
NEW QUESTION 111
You have the Microsoft Azure Advanced Threat Protection (ATP) workspace shown in the Workspace exhibit.
(Click the Workspace tab.)
The sensors settings for the workspace are configured as shown in the Sensors exhibit. (Click the Sensors tab.)
You need to ensure that Azure ATP stores data in Asia.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
Answer:
Explanation: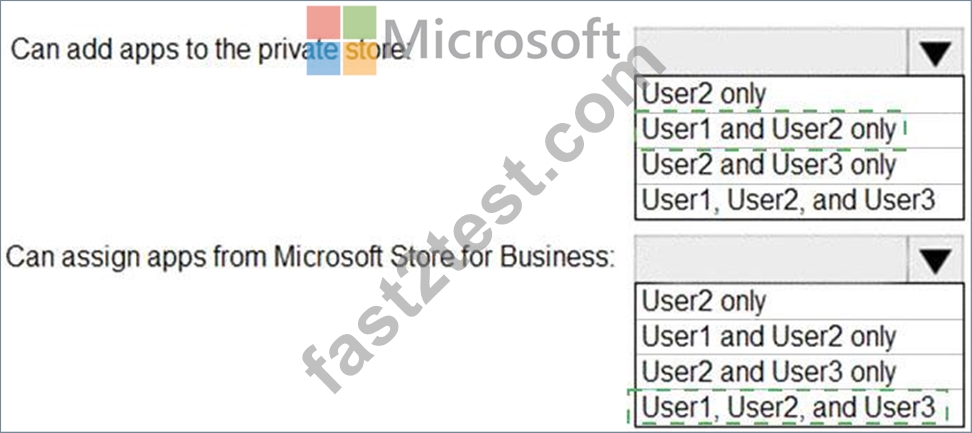
Explanation
https://docs.microsoft.com/en-us/azure-advanced-threat-protection/install-atp-step1
NEW QUESTION 112
From the Security & Compliance admin center, you create a content export as shown in the exhibit. (Click the Exhibit tab.)
What will be excluded from the export?
- A. a 10-MB XLSX file
- B. a 5-KB RTF file
- C. an 80-MB PPTX file
- D. a 5-MB MP3 file
Answer: D
Explanation:
Explanation
Unrecognized file formats are excluded from the search.
Certain types of files, such as Bitmap or MP3 files, don't contain content that can be indexed. As a result, the search indexing servers in Exchange and SharePoint don't perform full-text indexing on these types of files.
These types of files are considered to be unsupported file types.
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/partially-indexed-items-in-content-search?view=o36
https://docs.microsoft.com/en-us/office365/securitycompliance/export-a-content-search-report
NEW QUESTION 113
You have a Microsoft 365 subscription.
You create a Microsoft Cloud App Security policy named Risk1 based on the Logon from a risky IP address template as shown in the following exhibit.
You have two users named User1 and User2. Each user signs in to Microsoft SharePoint Online from a risky IP address 10 times within 24 hours.
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
NEW QUESTION 114
You need to meet the requirement for the legal department
Which three actions should you perform in sequence from the Security & Compliance admin center? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
Answer:
Explanation:
References:
https://www.sherweb.com/blog/ediscovery-office-365/
NEW QUESTION 115
You have a Microsoft 365 E5 subscription that contains two users named Admin1 and Admin2.
All users are assigned a Microsoft 365 Enterprise E5 license and auditing is turned on.
You create the audit retention policy shown in the exhibit. (Click the tab.)
After Policy1 is created, the following actions are performed:
* Admin1 creates a user named User1.
* Admin2 creates a user named User2.
How long will the audit events for the creation of User1 and User2 be retained? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation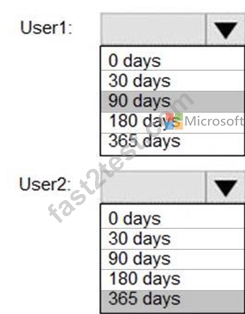
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/audit-log-retention-policies?view=o365-worldwide
NEW QUESTION 116
DRAG DROP
Your company has a Microsoft 365 E5 tenant.
Users access resources in the tenant by using both personal and company-owned Android devices. Company policies requires that the devices have a threat level of medium or lower to access Microsoft Exchange Online mailboxes.
You need to recommend a solution to identify the threat level of the devices and to control access of the devices to the resources.
What should you include in the solution for each device type? To answer, drag the appropriate components to the correct devices. Each component may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.
Select and Place:
Answer:
Explanation:
Section: [none]
NEW QUESTION 117
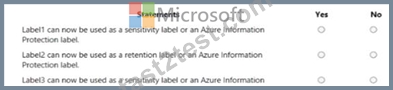
Your company has a Microsoft 365 subscription that uses an Azure Active Directory (Azure AD) tenant named contoso.com. The company stores 2 TBs of data in SharePoint Online document libraries. The tenant has the labels shown in the following table.
Answer:
Explanation: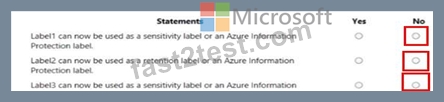
NEW QUESTION 118
......
The MS-101: Microsoft 365 Mobility & Security exam is associated with the Microsoft 365 Certified: Enterprise Administrator Expert certification. This test is designed for the Microsoft 365 Enterprise Administrators with the relevant skills in planning, deploying, handling, migrating, and assessing Microsoft 365 services. These specialists carry out the management tasks related to Microsoft 365 tenant for the enterprises, which include its supporting technologies, identities, compliance, and security.
MS-101 certification guide Q&A from Training Expert Fast2test: https://www.fast2test.com/MS-101-premium-file.html
The Best Microsoft 365 Study Guide for the MS-101 Exam: https://drive.google.com/open?id=1MdkEp6moxkCIQFfXXINhfEc9Ga12d_1X